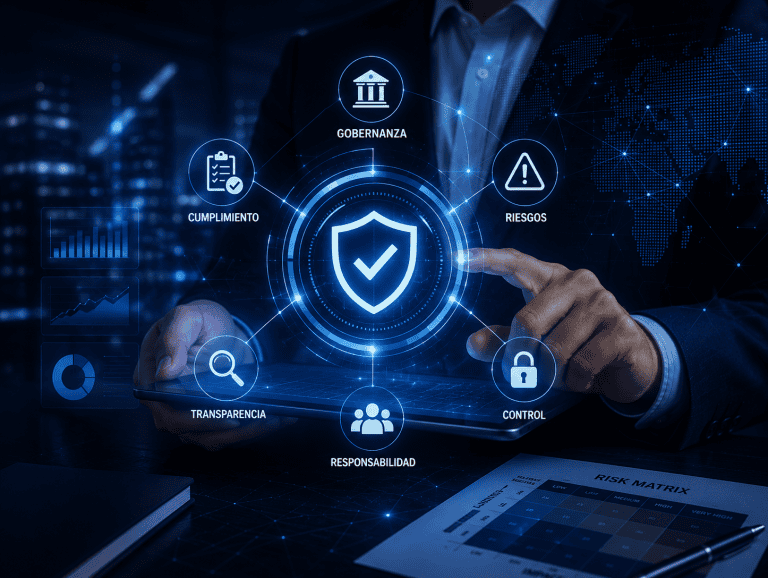
We strengthen governance, risk management, and regulatory compliance to support informed decisions and resilient business operations.
We help organizations strengthen corporate governance, manage enterprise risk, and support regulatory compliance through an integrated Governance, Risk, and Compliance (GRC) approach. We help identify risks, define effective controls, and enable informed decision-making based on reliable business insights.
We combine IT governance, risk assessments, control management, policy management, audit practices, and executive dashboards to strengthen oversight of critical business processes. Our approach integrates recognized frameworks, meaningful metrics, and governance practices that improve visibility, traceability, and continuous improvement.
We support the evolution of your Governance, Risk, and Compliance (GRC) framework to adapt to changing regulations, improve compliance management, and strengthen organizational resilience. We build governance models designed to evolve with your business and an ever-changing regulatory landscape.
How we deliver
We operate with a DevOps culture and a continuous improvement mindset, delivering frequent releases, measuring software quality through actionable metrics, and maintaining a transparent rework rate that we can demonstrate for every project.
Iterative deliveries that provide tangible results starting from the very first weeks.
Every release undergoes automated and manual testing, risk-based quality validation, code reviews, and dependency analysis to ensure reliability, security, and production readiness.
Process automation to reduce time to market.
We apply security standards from the very first architectural phase to protect your most valuable asset: information.